DPDP Compliance &
Cybersecurity Consulting
End-to-end DPDP Act compliance, cybersecurity consulting, and AI-powered automation, so you can innovate without compromise.
 ISO 27001
 SOC 2
 PCI DSS
 GDPR
 NIST
 CIS
 DORA
Compliance is complex. It doesn't have to be slow
Most organizations struggle with fragmented security programs, manual compliance processes, and vendor risk blind spots.
Fragmented security programs
Tools and teams that don't talk. Gaps hide between them.
Manual compliance processes
Spreadsheet-driven evidence collection that breaks at audit time.
Vendor risk blind spots
One-time questionnaires aren't enough. Risk is continuous.
AI introduced too fast
Shadow GenAI usage outpacing your governance.
End-to-end security & compliance
Five focused practice areas. Most clients combine 2–3 for comprehensive coverage.
AI Security
Govern AI use, secure GenAI deployments, and align to ISO 42001 & NIST AI RMF.
Explore AI SecurityCloud Security
Hardening across AWS, Azure, and GCP: CSPM, IAM, Zero Trust.
Explore Cloud SecurityVendor Risk (TPRM)
Continuous third-party assurance, AI Trust Center, automated questionnaires.
Explore Vendor Risk (TPRM)Operational Resilience
BCM, DR, and impact tolerance, ready for DORA and RBI guidance.
Explore Operational ResilienceIS GRC
ISO 27001, SOC 2, NIST, PCI DSS, GDPR: readiness through certification.
Explore IS GRCDPDPA Compliance
End-to-end readiness for the Digital Personal Data Protection Act 2023 and DPDP Rules 2025.
Explore DPDPA ComplianceConsent Management
Tamper-evident consent artefacts, multilingual notices, one-click withdrawal. Built for the DPDP Act.
Explore Consent ManagementPlatform
AI-powered automation that replaces recurring consultant spend.
Explore the platformWorking in a regulated sector? See how we tailor these to your industry.
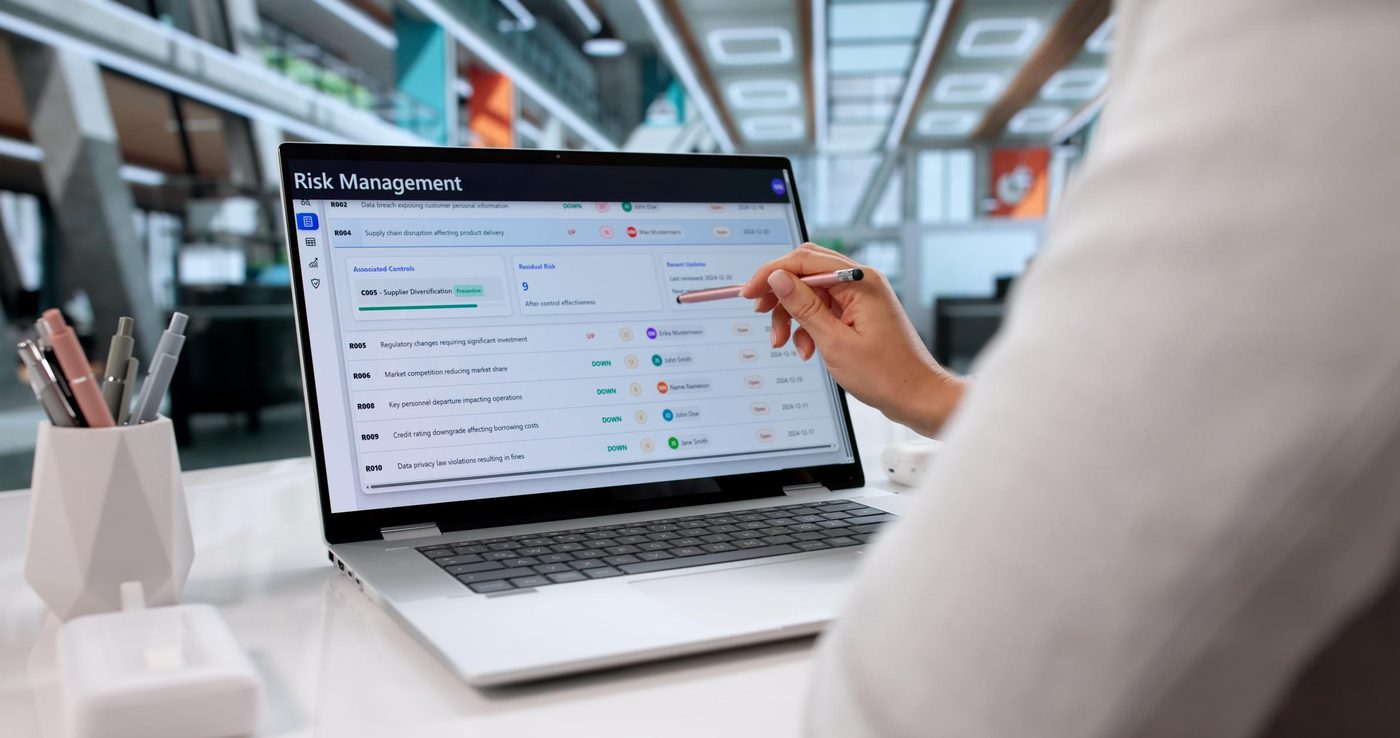
 ORB Platform
AI-Powered Unified Operating Solution
Manage your risk and compliance with a single, always-on platform.
A partner, not a vendor
Outcome-driven engagements with shared accountability. Built for regulatory scrutiny.
Partner, Not Vendor
Outcome-driven with shared accountability across every engagement.
Audit-Ready
Every artifact built to withstand regulatory scrutiny on day one.
AI + Human
Platform augments, not replaces, senior consulting expertise.
Global Standards
ISO 27001, SOC 2, NIST, GDPR, PCI DSS, and growing.
What partners are saying
OrbCyber compressed our SOC 2 readiness from twelve months to ten weeks. The artifacts held up perfectly under audit.
Platform replaced what used to be a quarterly consulting cycle with a continuous dashboard. We never go dark on vendor risk.
They challenged us where it counted, then built. Genuinely felt like an extension of the team rather than an external firm.
Ready to strengthen your security posture?
Book a free 30-minute consultation. No slides, just a working conversation about your gaps and roadmap.